
Mobile Security & Subscriber Protection
Covering SIM swap fraud prevention, mobile money security, 2FA/OTP protection, and the on-device technologies that protect subscribers at the absolute edge of the network—where identity is most vulnerable and stakes are highest.
A fraudulent call blocked after it connects has already done its job. For carrier fraud and revenue assurance teams, that’s the uncomfortable truth most defenses still ignore. For carrier fraud and revenue assurance teams watching Wangiri fraud spike again in 2026, that’s the current state of most existing defenses: networks built to analyze what already […]
The human impact of telecom fraud hits seniors, small businesses, and emerging markets hardest. These are the people behind the statistics.
AI voice phishing is reshaping telecom fraud. Discover how deepfake dialers break trust and how behavioral detection restores security.
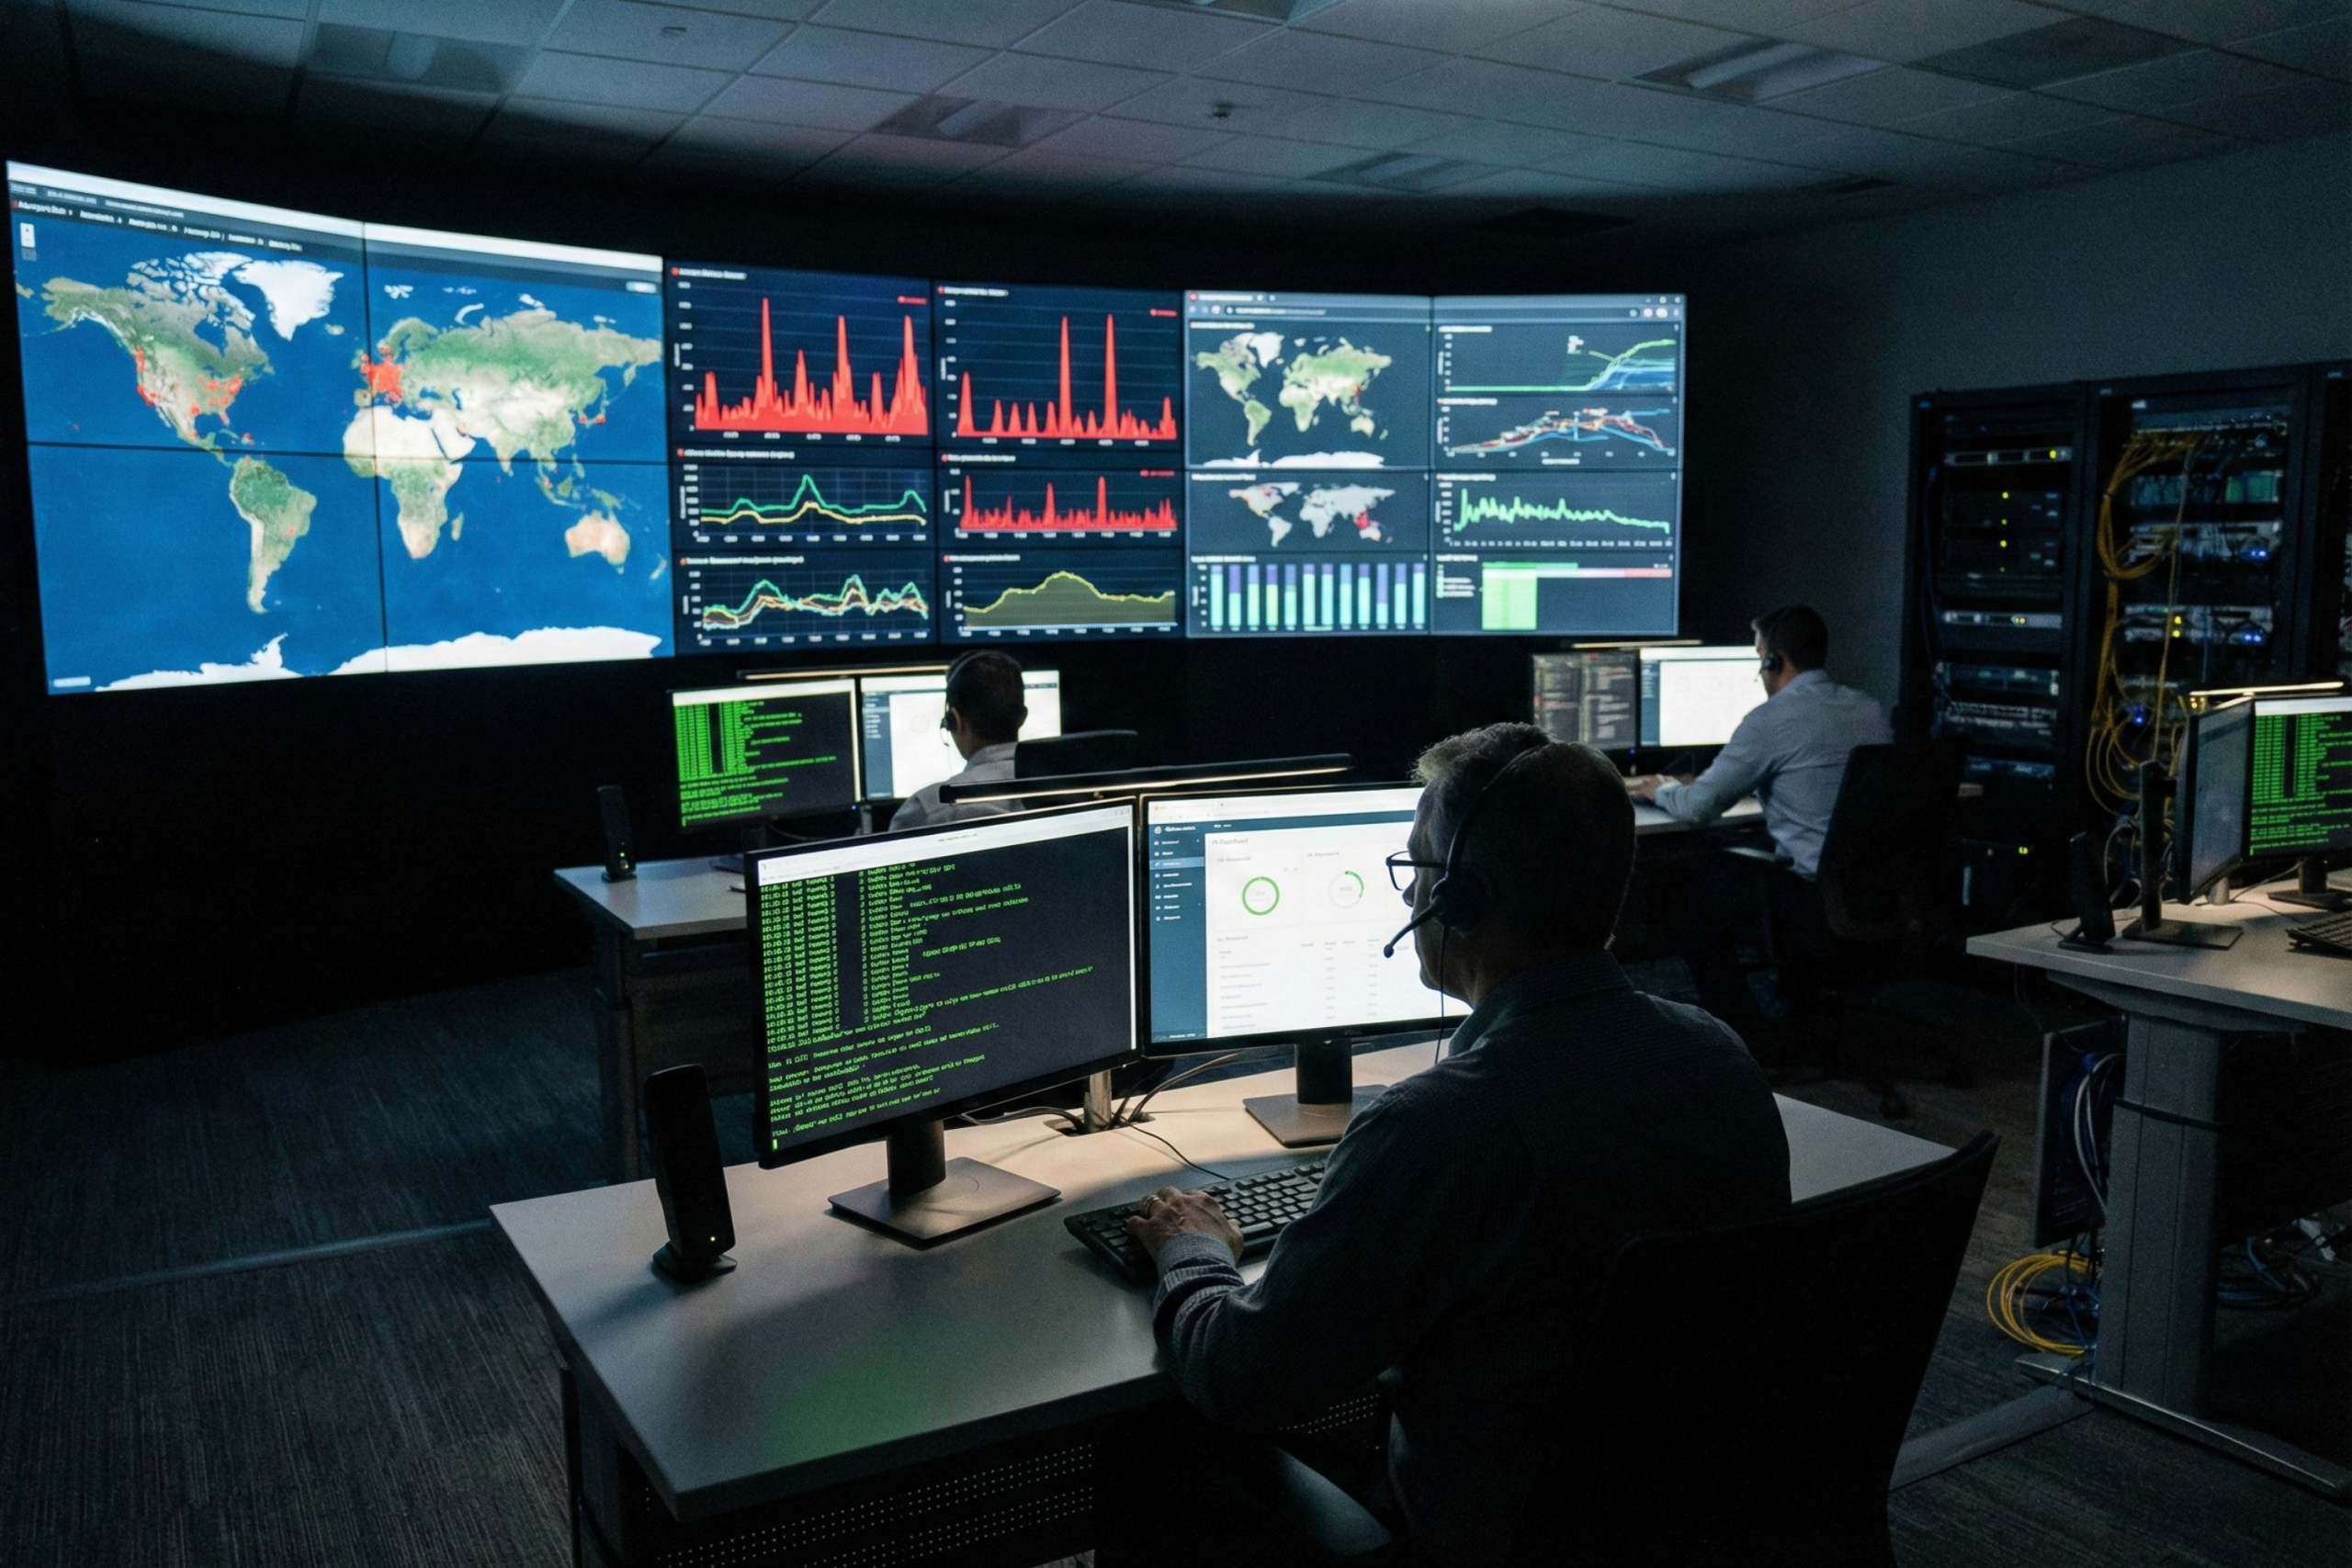
It is 2:17 a.m. in the network operations center. Two alarms are live. A legacy TDM interconnect is degrading on one screen while an IP trunk holds steady on another. Fraud flags are spiking at the boundary between them, and nobody wants to be the engineer who called the cutover too early. This is the […]
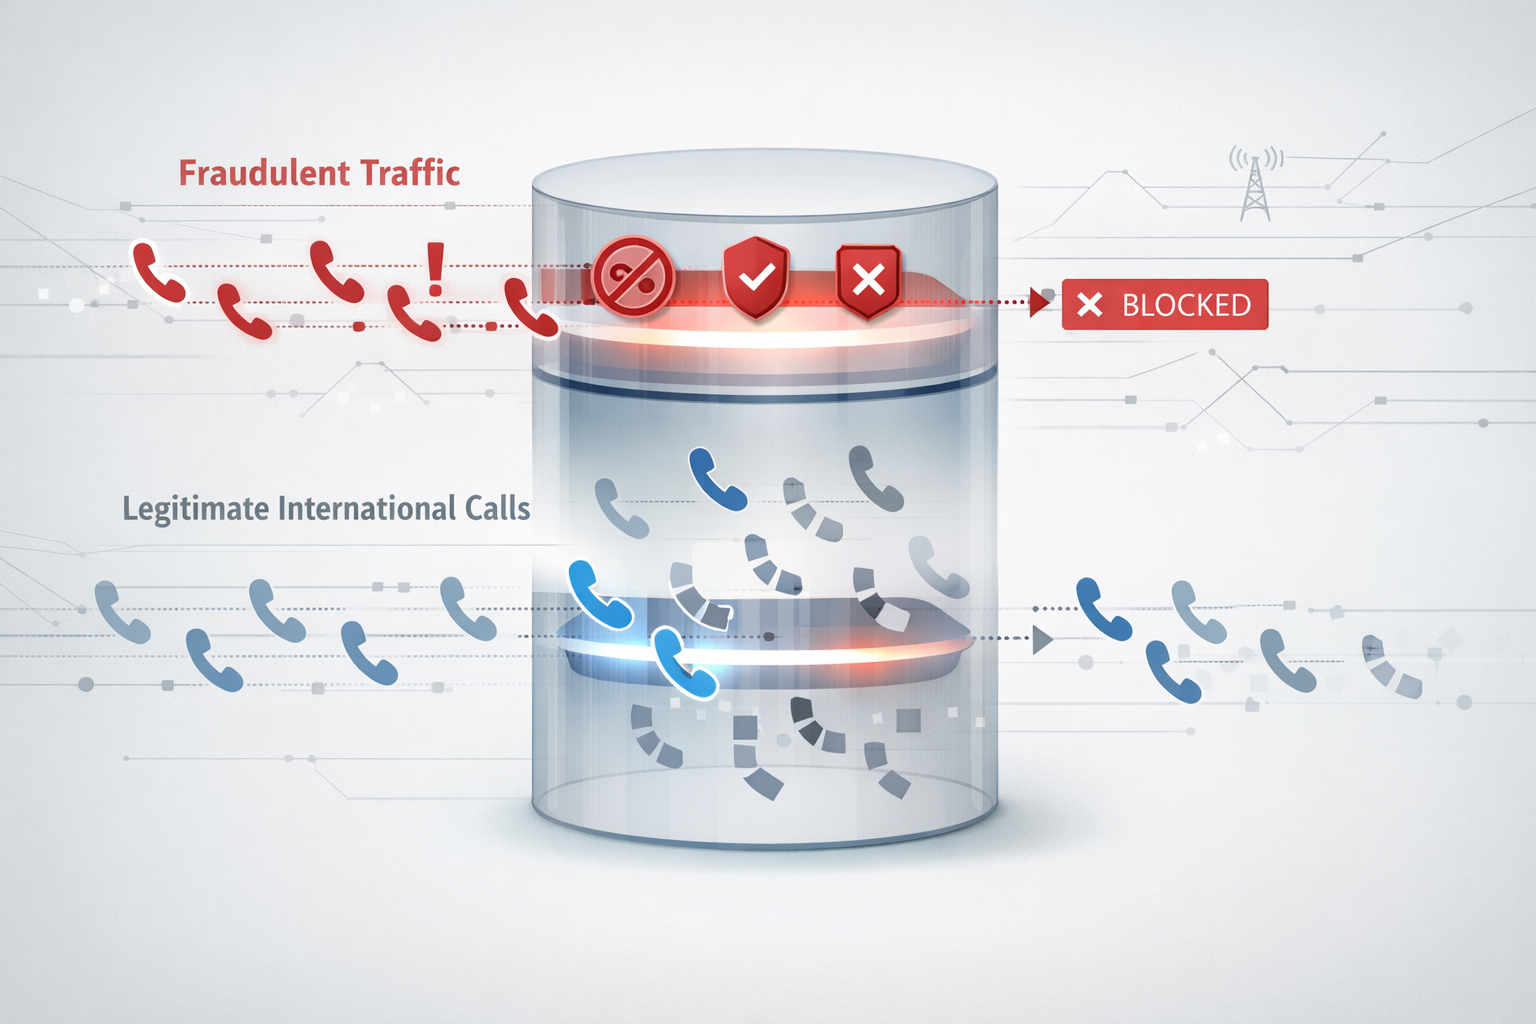
Your network operations center receives an alert at 3 AM: unusual call volume from Nigeria routing through a European interconnect. The CLI is properly formatted, call durations average 90 seconds, and the traffic profile matches a known enterprise customer’s campaign. Do you block it and risk angering a paying client? Or let it through and […]
Why Header Data Doesn’t Tell the Whole Story Let’s pull back the curtain on something that looks simple—but isn’t. Attestation labels (A, B, C) from the STIR/SHAKEN framework may offer a quick snapshot of a call’s trust level, but they don’t guarantee full authentication. These tags can be spoofed, allowing fraudulent calls to slip through […]
- 1
- 2